
On September 7, Gilles Seghaier, Julien Allaix and I had the opportunity to speak at fwd:cloudsec Europe 2026 in London with our talk, "Multi-Cloud Was Supposed to Be Resilient, Until We Tried to Secure It."
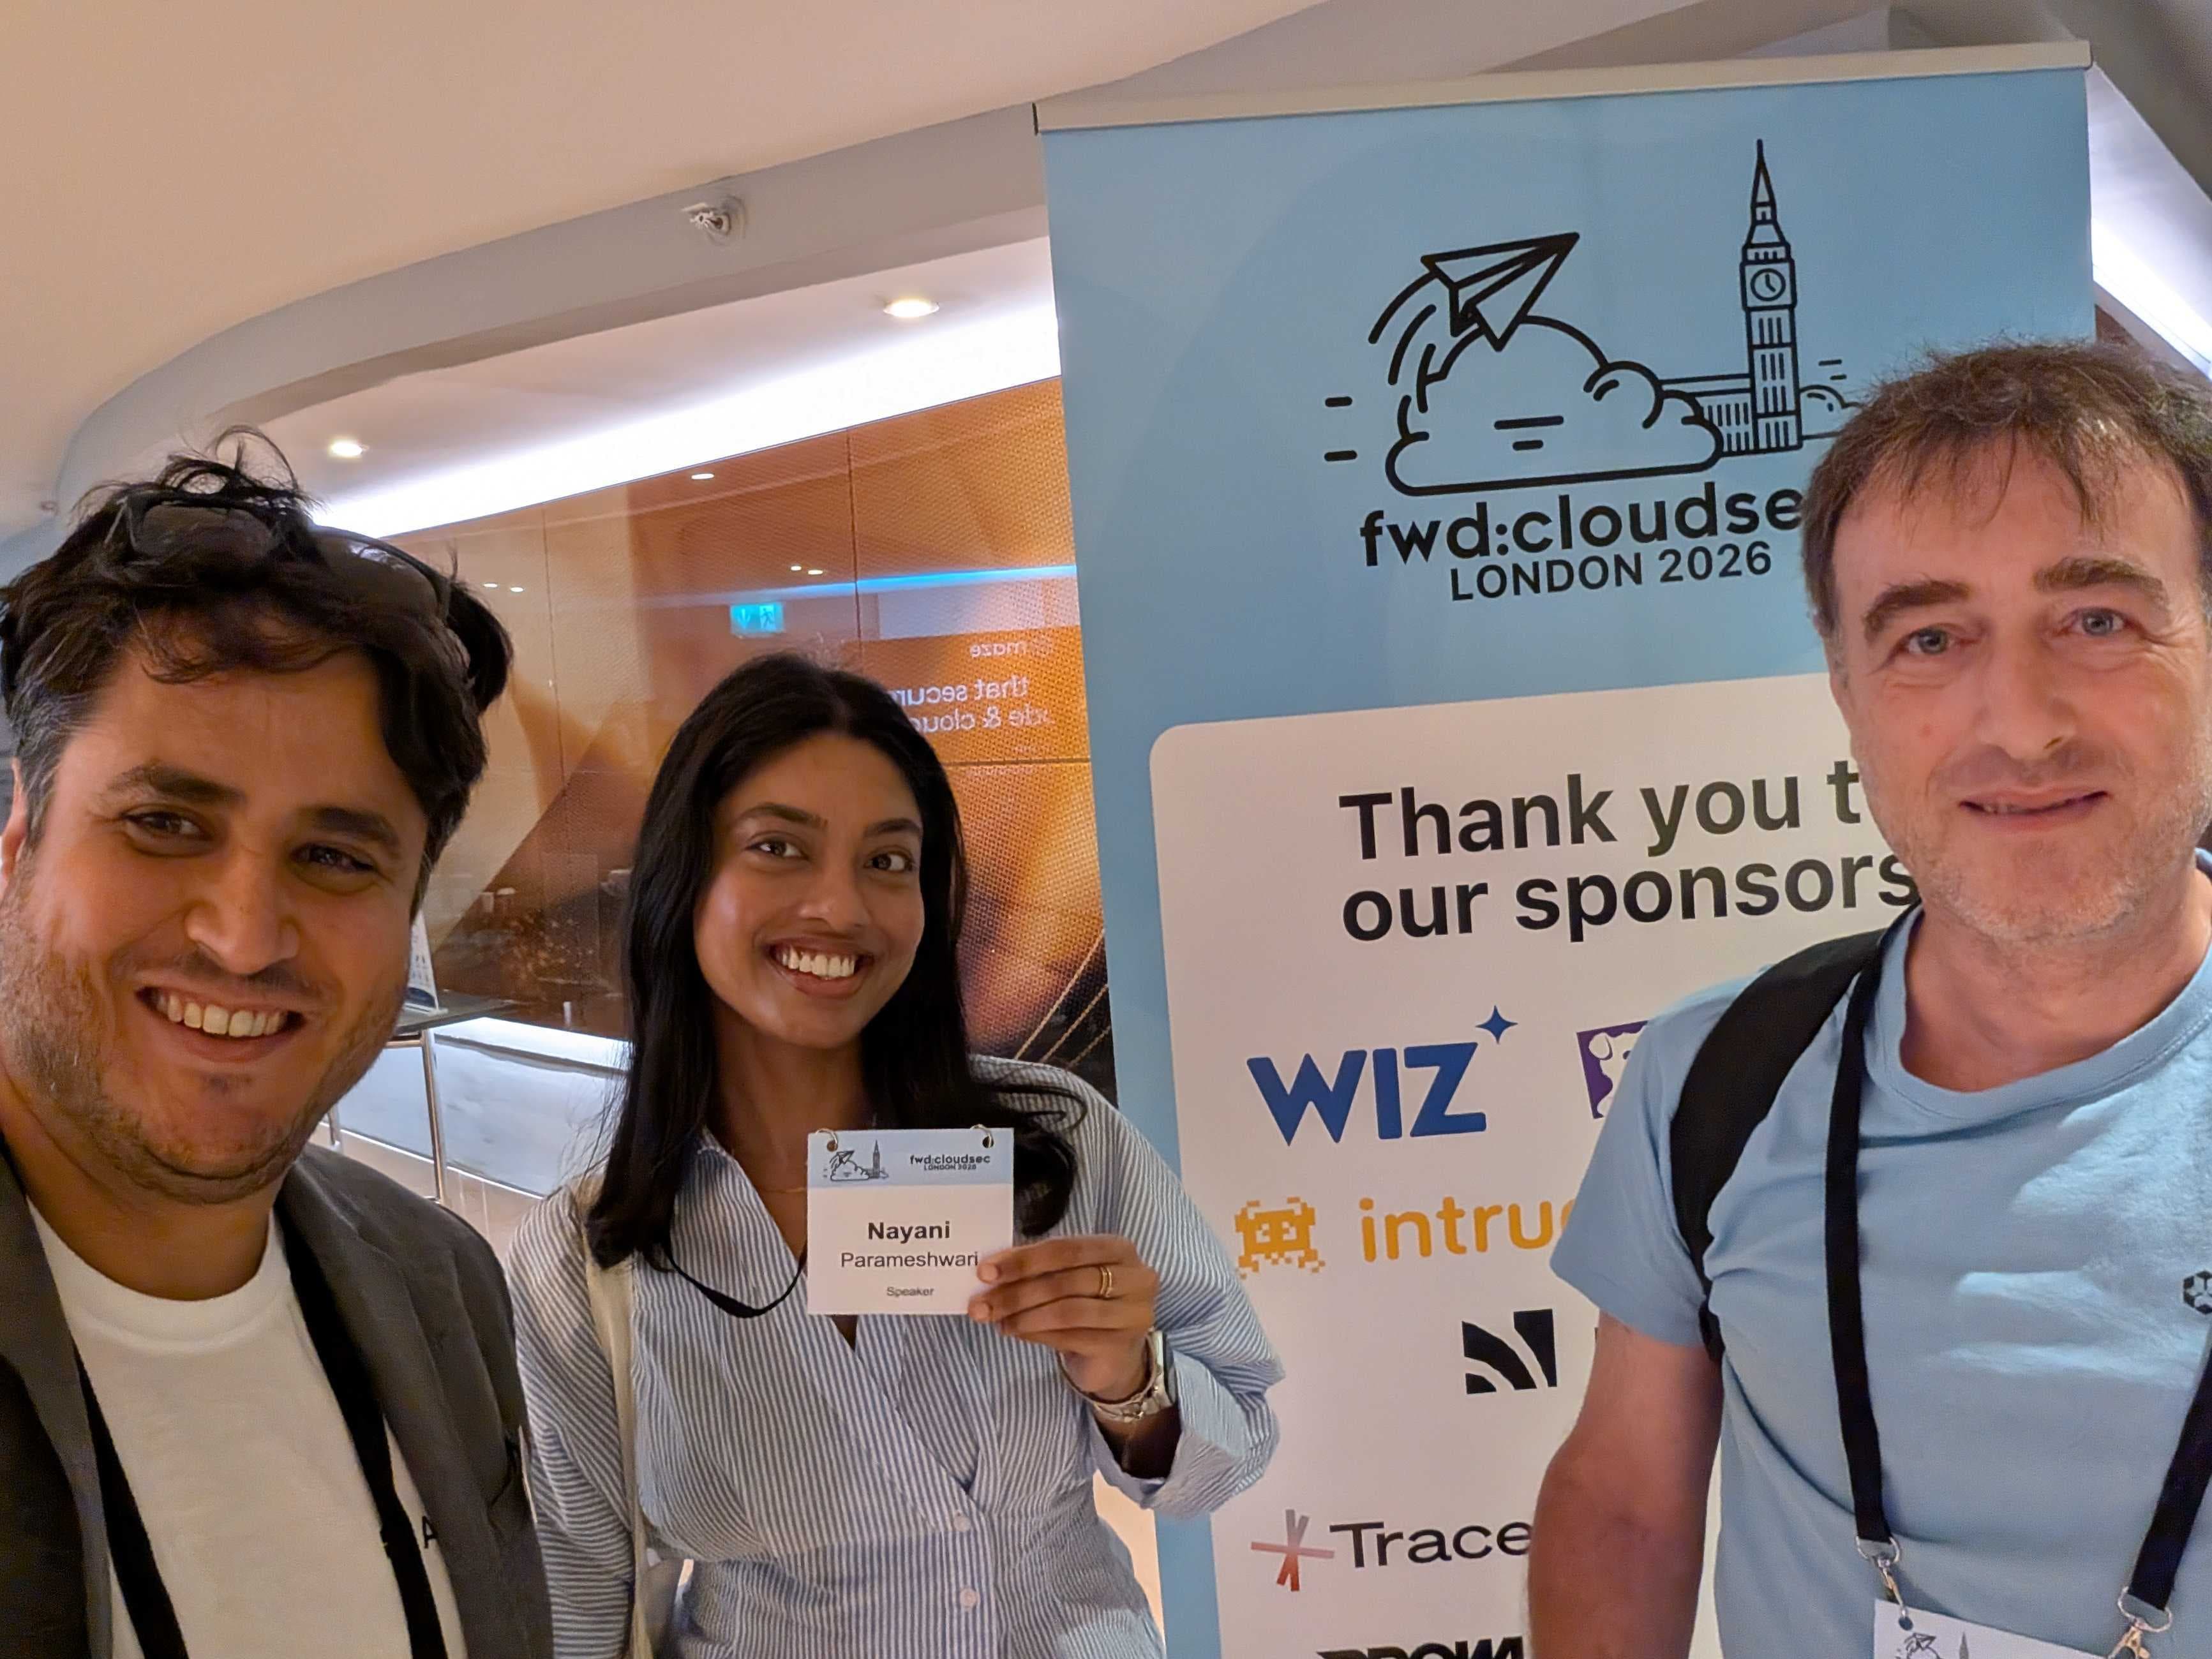
On September 7, Gilles Seghaier, Julien Allaix and I had the opportunity to speak at fwd:cloudsec Europe 2026 in London with our talk, “Multi-Cloud Was Supposed to Be Resilient, Until We Tried to Secure It.”
Our goal was to share what multi-cloud security looks like when you move beyond architecture diagrams and operate it in production.
We presented three challenges we encountered at ASTRAN. At the edge layer, maintaining our confidentiality requirements while providing load balancing, DDoS protection and WAF capabilities introduced unexpected technical trade-offs. For data storage, we showed how S3 and SigV4 provide a relatively common model across several providers, while Azure Blob requires a different API and authentication approach. Finally, we discussed secrets management and how centralizing secrets becomes much more complicated once services cross cloud boundaries.
It was a great opportunity to represent ASTRAN, share lessons from our experience, and exchange ideas with the cloud security community in London.
A big thank you to the fwd:cloudsec team and everyone who joined our session! ☁️🔐